Zero Trust Architecture
A security model where no user, device, or network flow is trusted by default — inside the perimeter or outside it. Each session is verified and authorized before access is granted, then re-evaluated continuously.
Cybersecurity Infographic Series · Network and Infrastructure Security
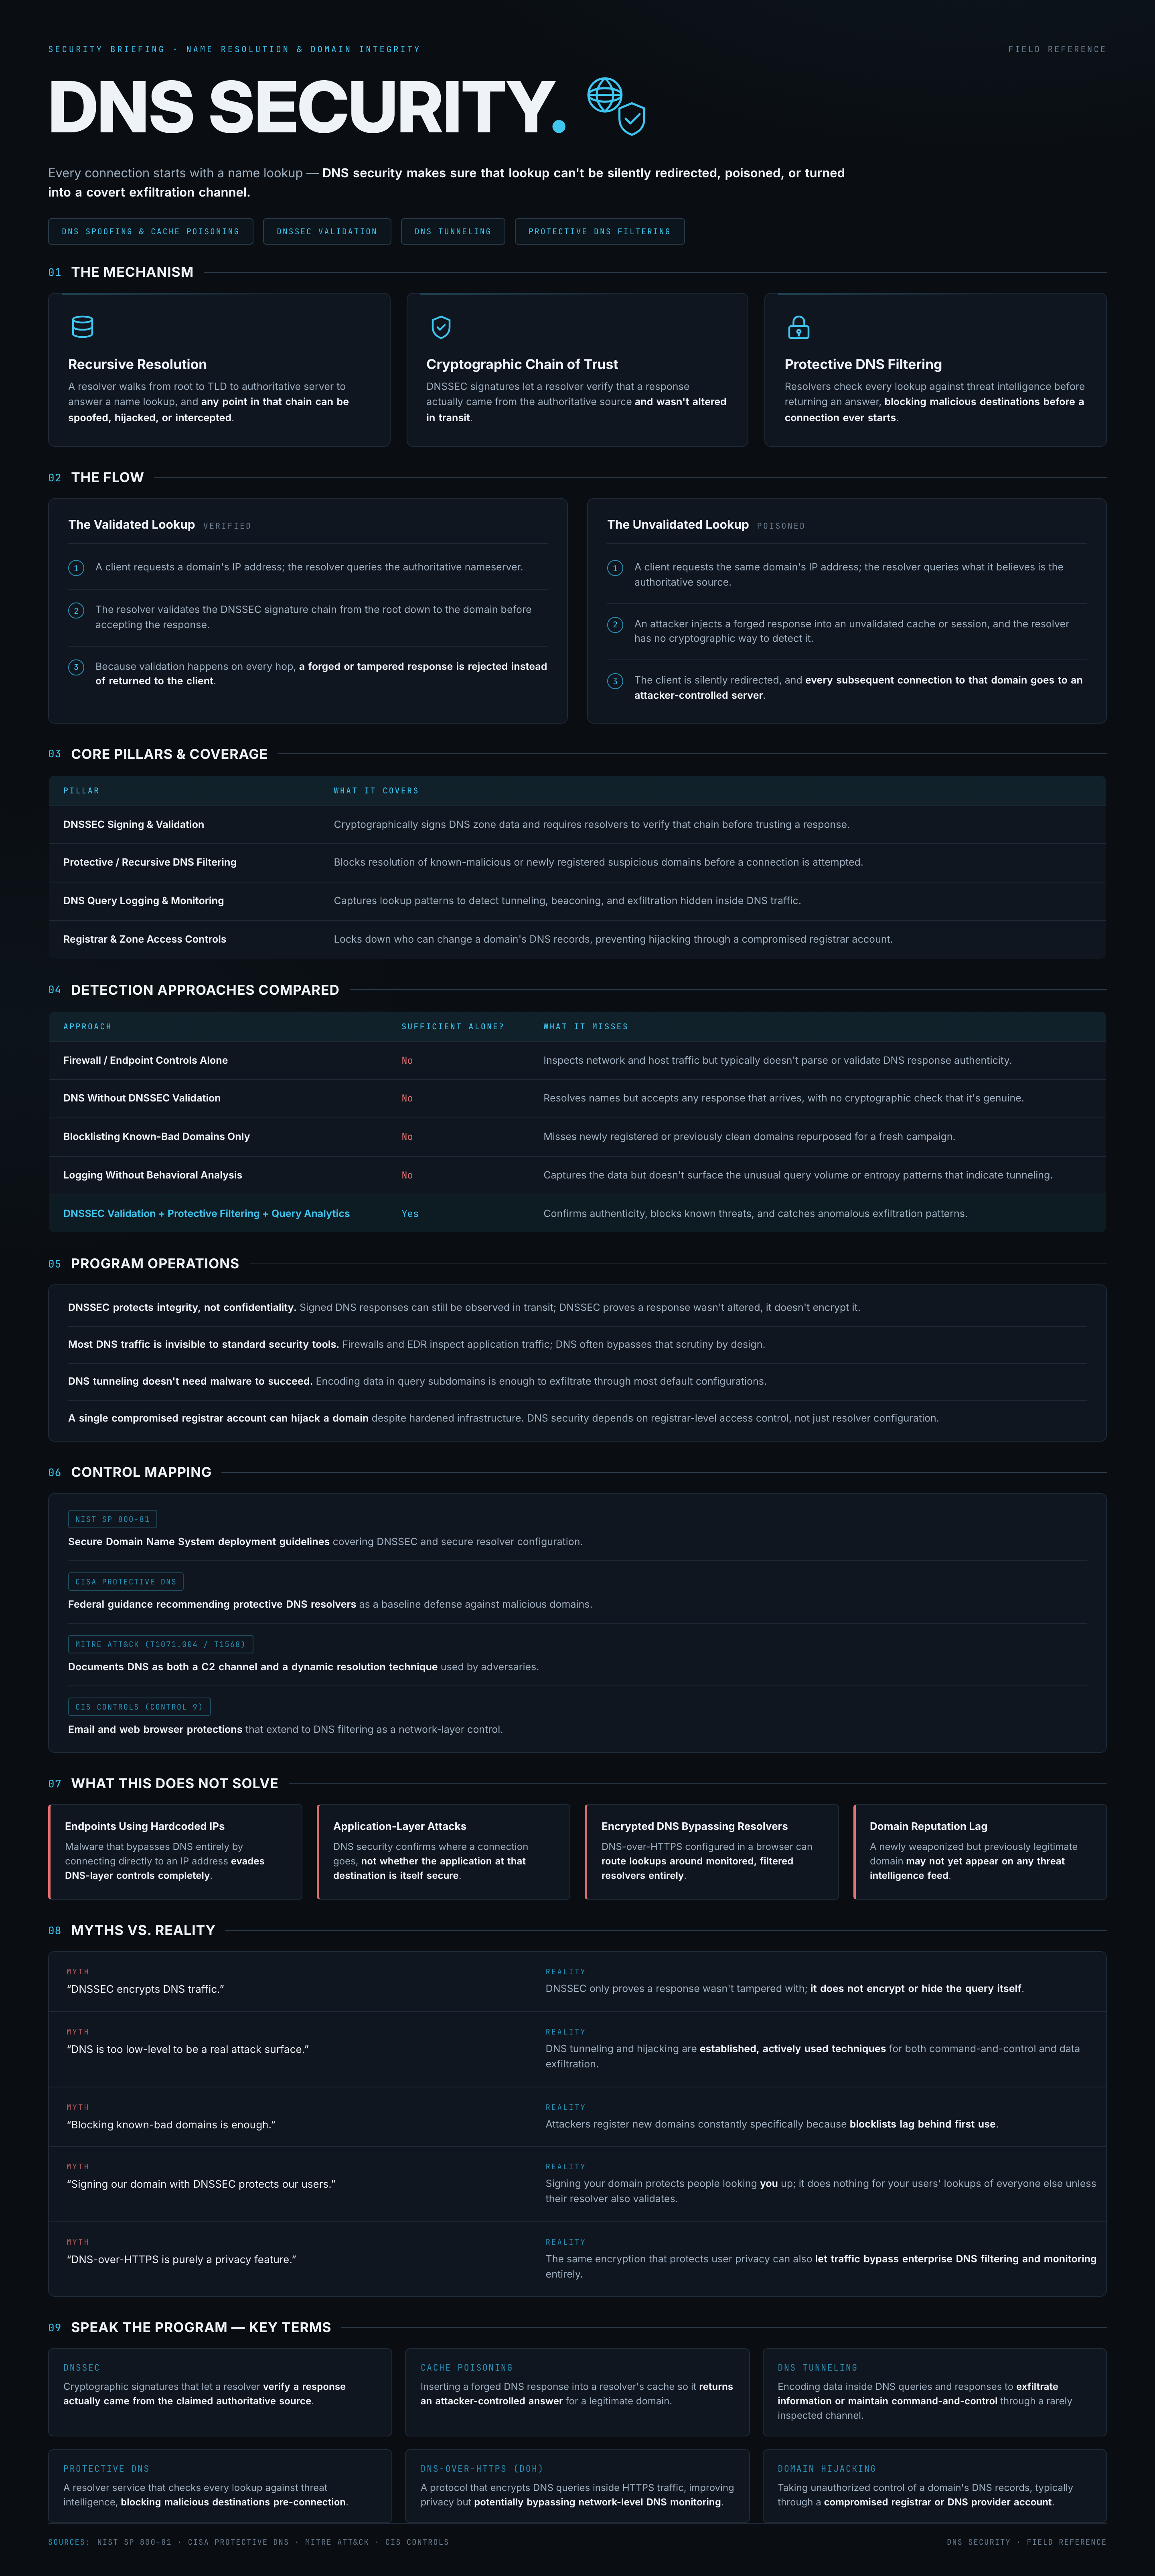
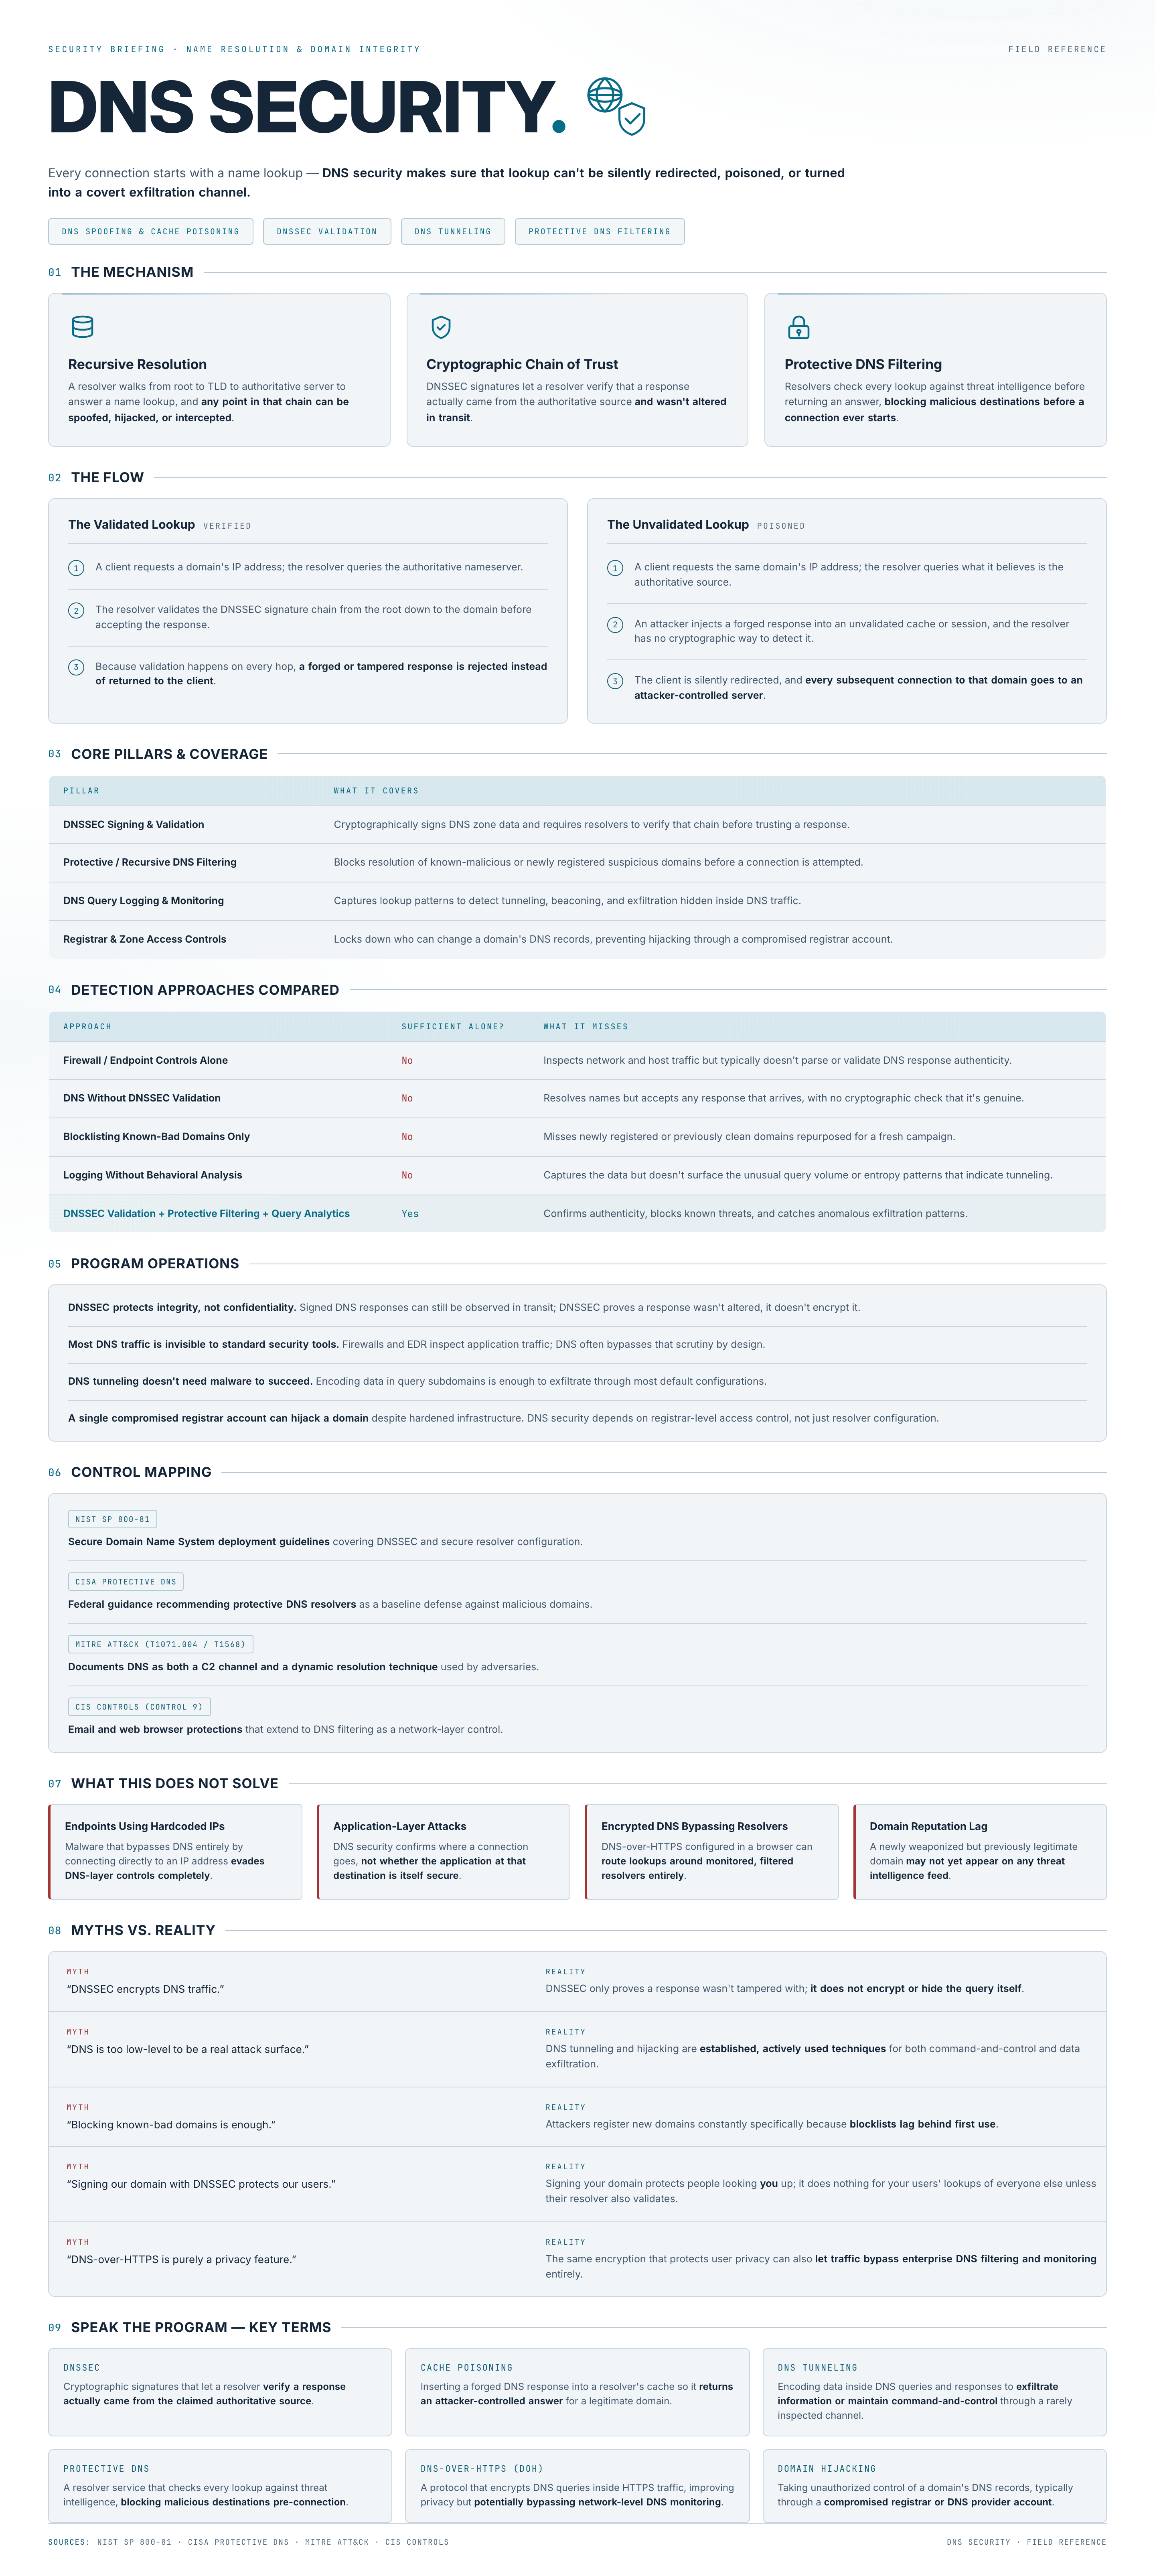
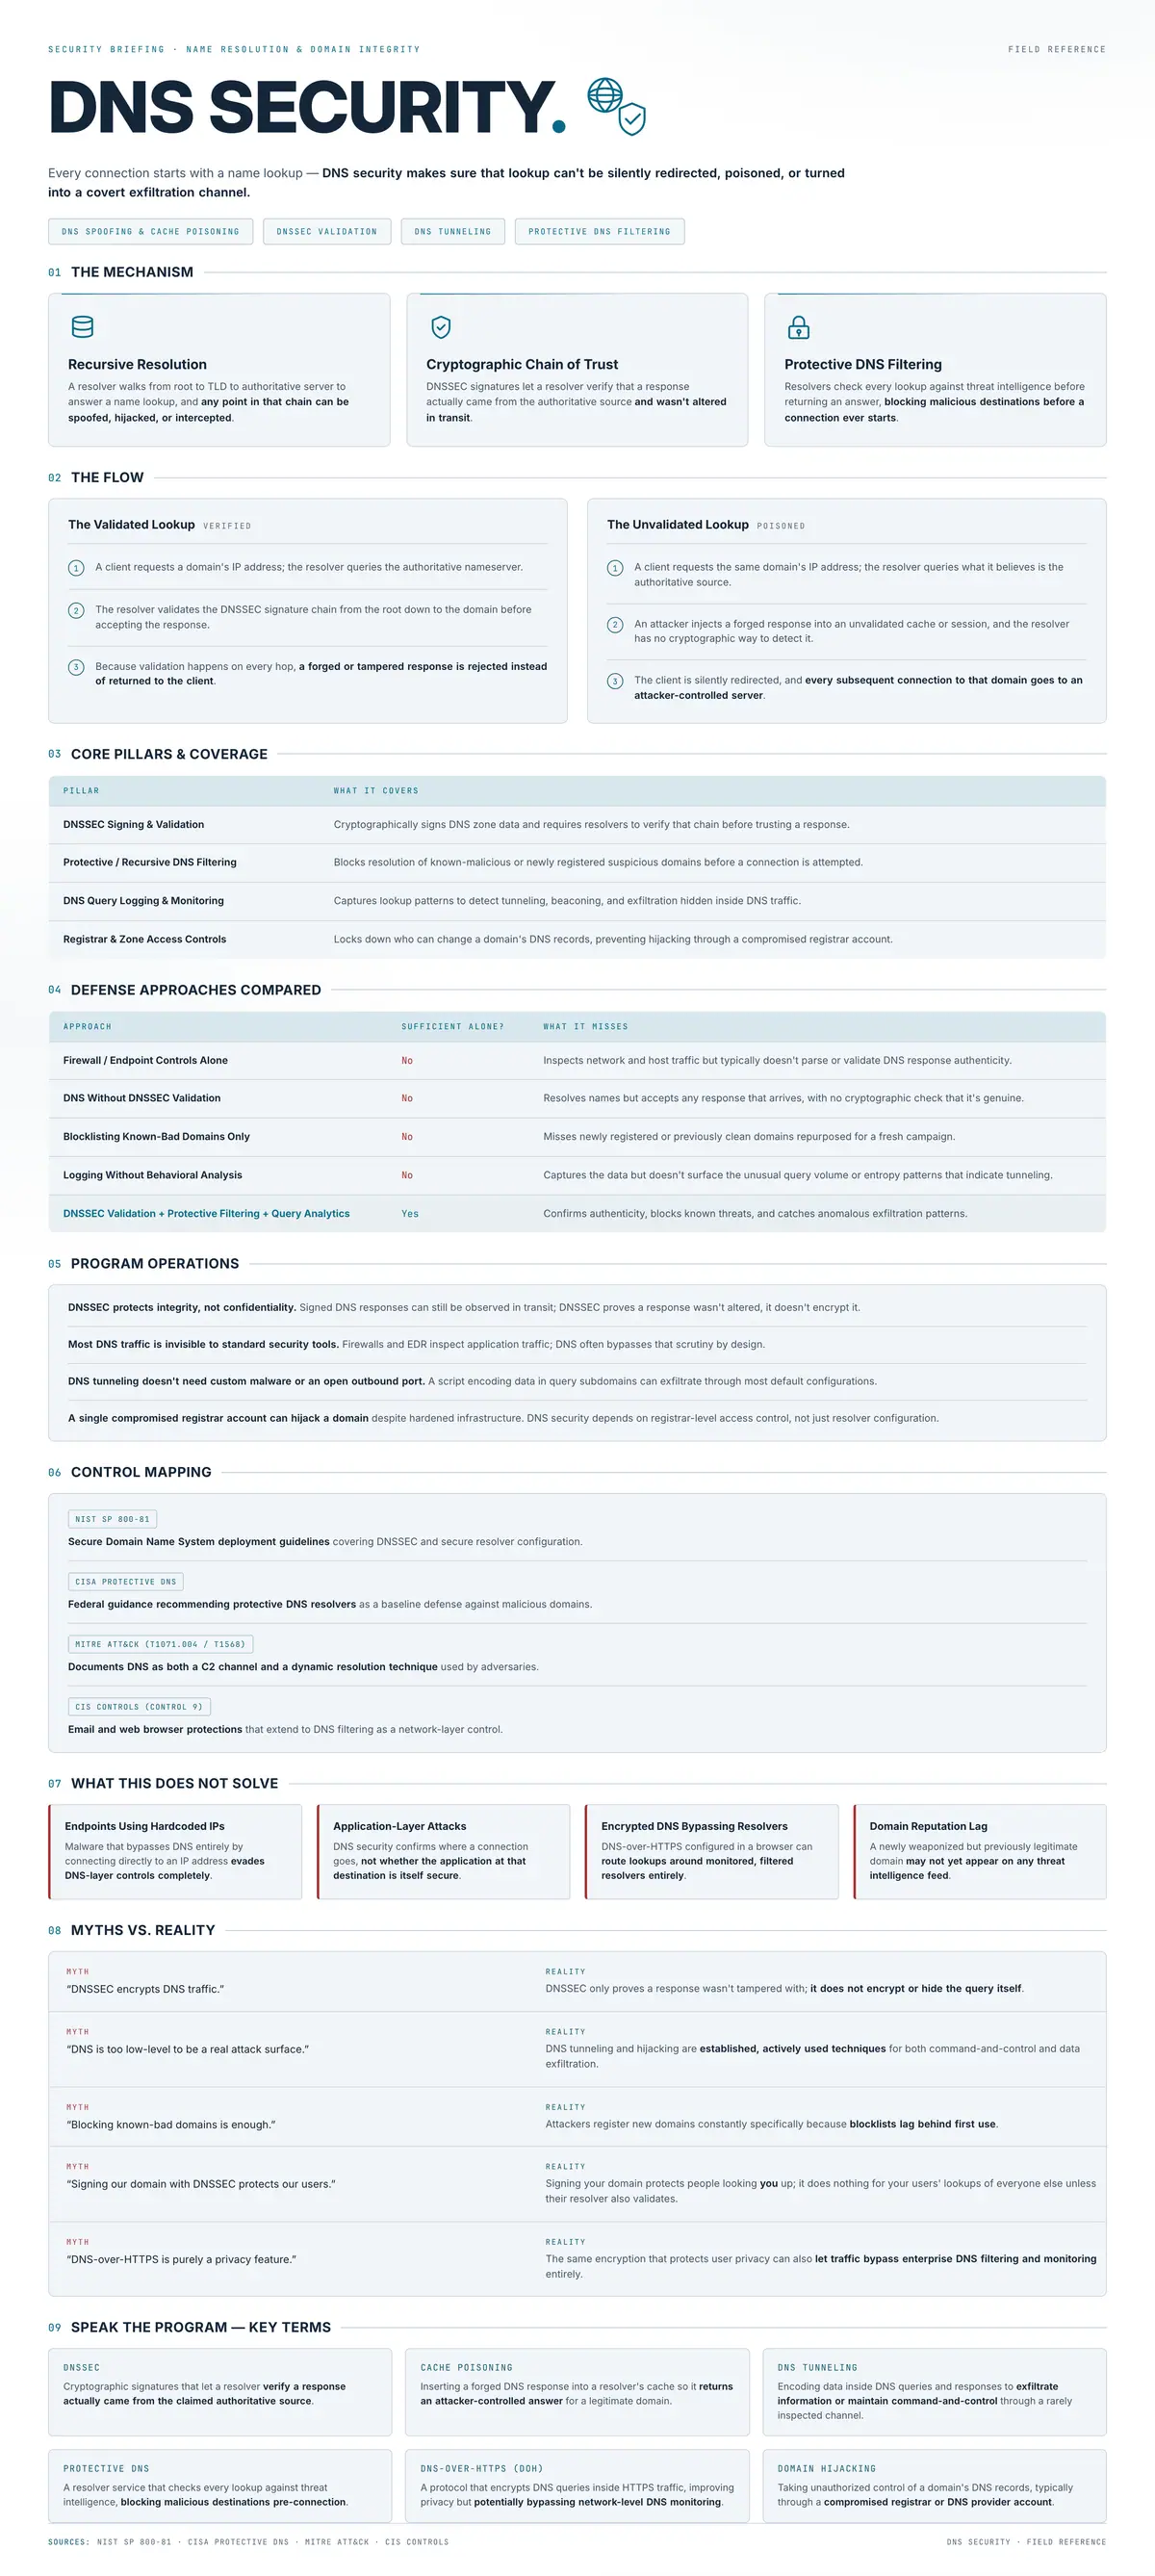
Every connection starts with a name lookup — DNS security makes sure that lookup can't be silently redirected, poisoned, or turned into a covert exfiltration channel.
A security model where no user, device, or network flow is trusted by default — inside the perimeter or outside it. Each session is verified and authorized before access is granted, then re-evaluated continuously.
VPN gateways are internet-facing, always-on, and rarely patched on schedule — making them one of the most exploited entry points into corporate networks. From split-tunneling misconfigurations to unpatched appliance CVEs, a poorly governed VPN becomes the front door attackers actually use.
A flat network lets one compromised device reach everything else — microsegmentation contains the blast radius so a breach cannot spread into the next zone.
Operational technology runs the physical world — valves, turbines, breakers, pumps — so a compromise isn't just a data-loss event. Safety and availability outrank confidentiality here, and the controls that work in IT can crash the equipment they're meant to protect.
5G's shared, software-defined core turns network slicing and inter-carrier signaling into the new attack surface — isolation between slices and trust between carriers must be continuously verified, not just assumed by design.
Zero trust replaces a single perimeter check with continuous verification of every request — network location stops implying trust, and identity, device posture, and policy decide access instead.