Cybersecurity Infographic Series · Threat Detection and Incident Response
Endpoint Detection and Response (EDR-XDR)
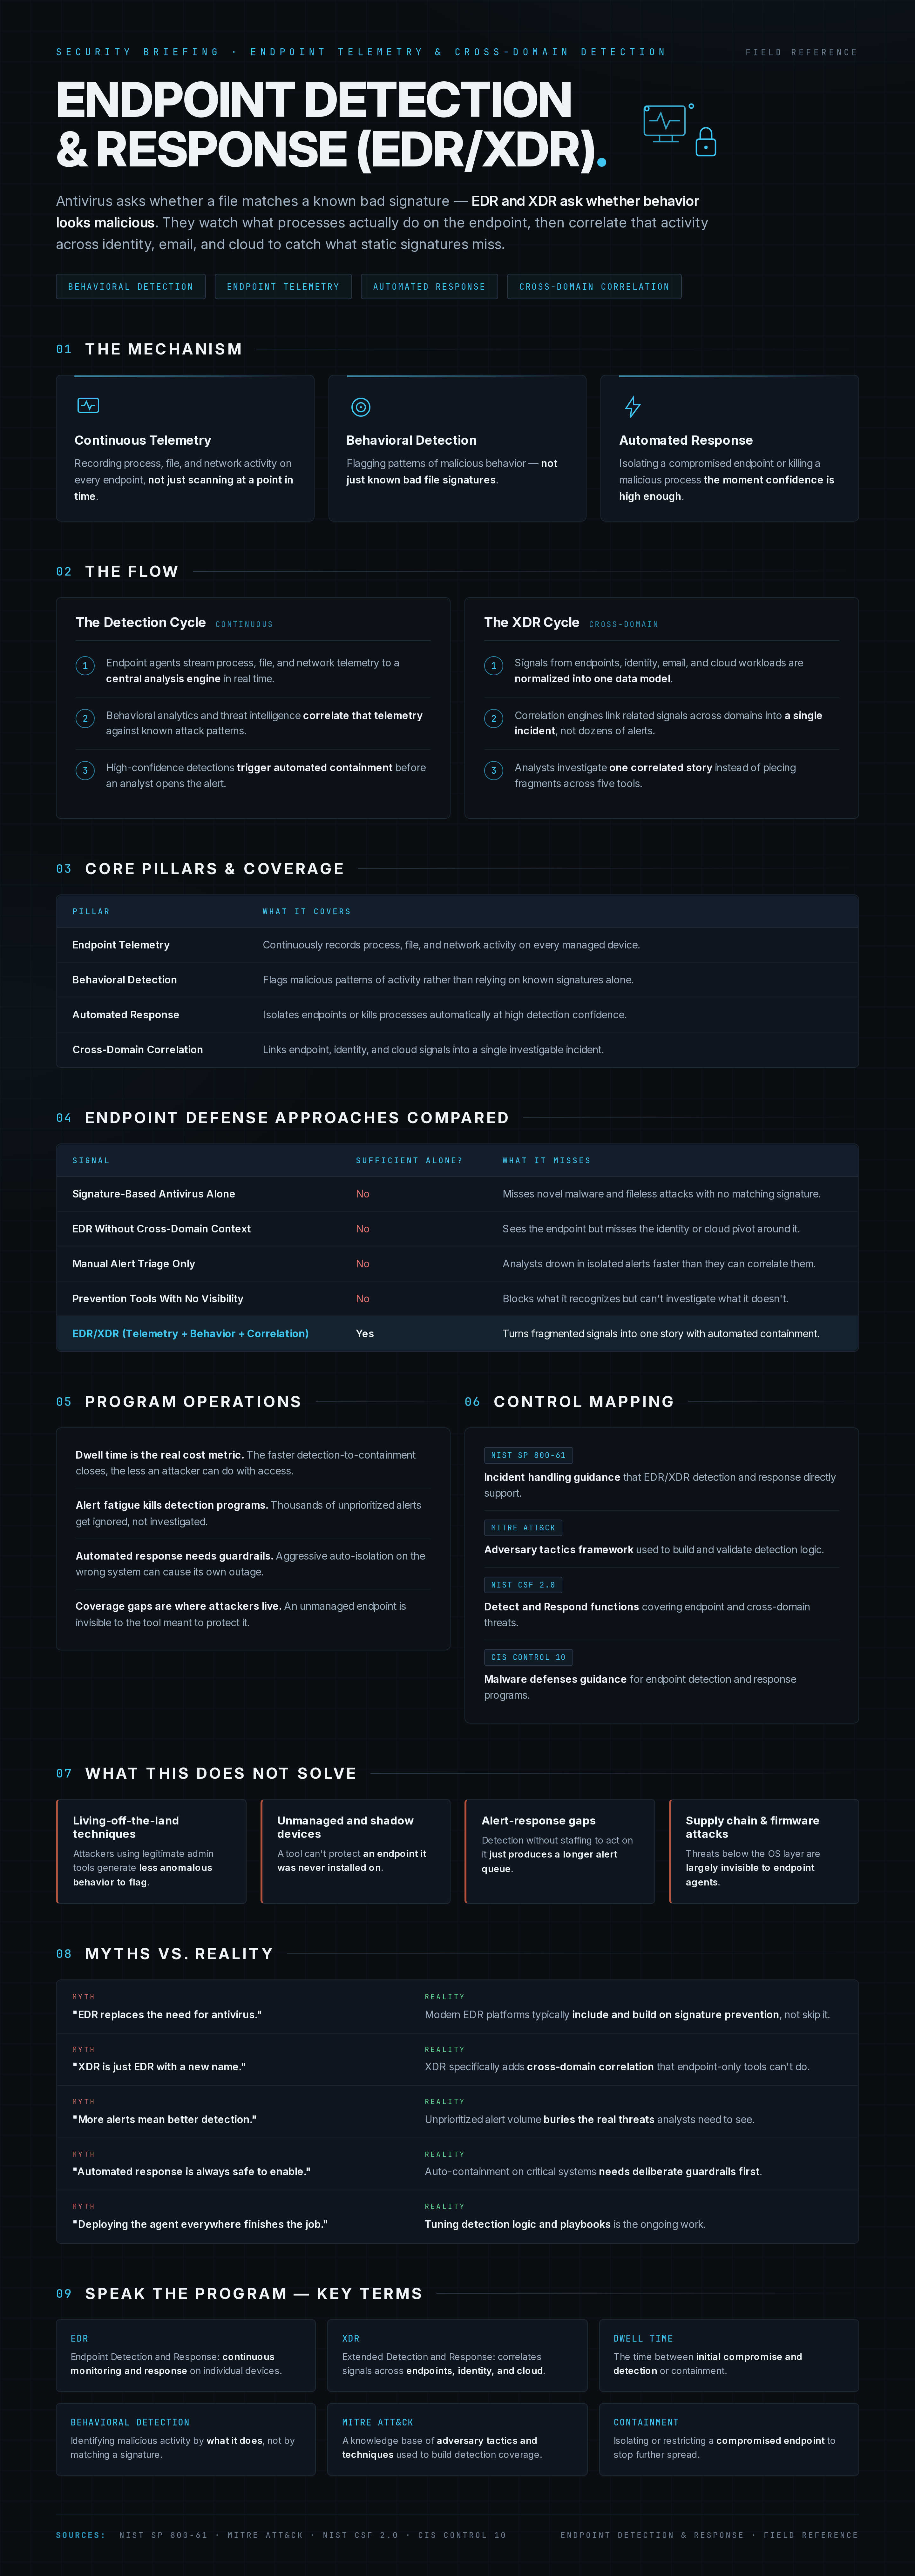
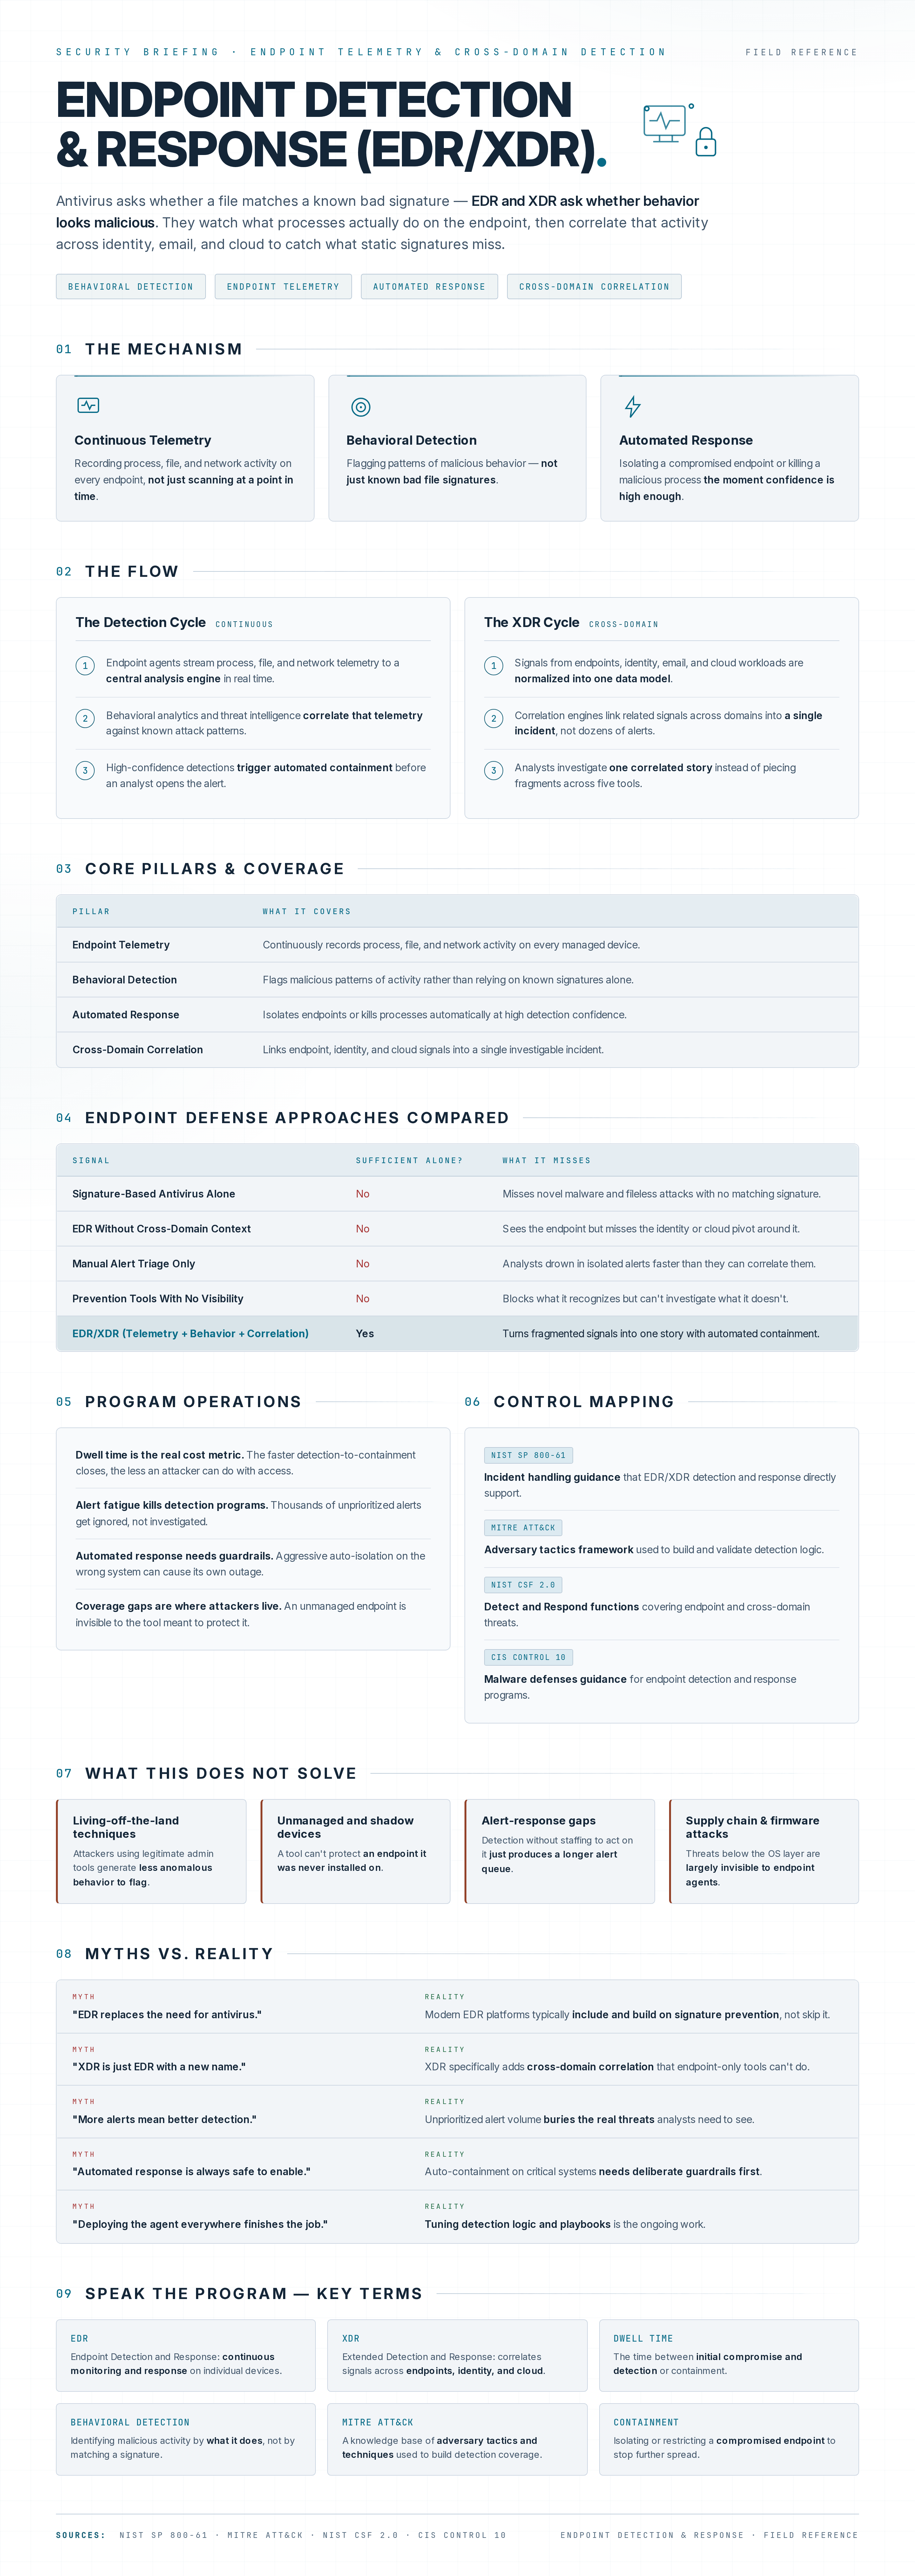
Antivirus asks whether a file matches a known bad signature — EDR and XDR ask whether behavior looks malicious. They watch what processes actually do on the endpoint, then correlate that activity across identity, email, and cloud to catch what static signatures miss.
Downloads
- Infographic (PNG, 2880×8110, 1.3 MB)
- Field reference (PDF, 2 sheets, 444 KB)
- Infographic, light edition (PNG, 1.2 MB)
- Field reference, light edition (PDF, 453 KB)
Free to download, no sign-up. Topic 17 of 91 in the series.