Passkeys
Phishing-resistant authentication built on public-key cryptography. The private key never reaches the server, syncs only end-to-end encrypted, and cannot be replayed by an attacker who captures the traffic.
Cybersecurity Infographic Series · Identity and Access Security
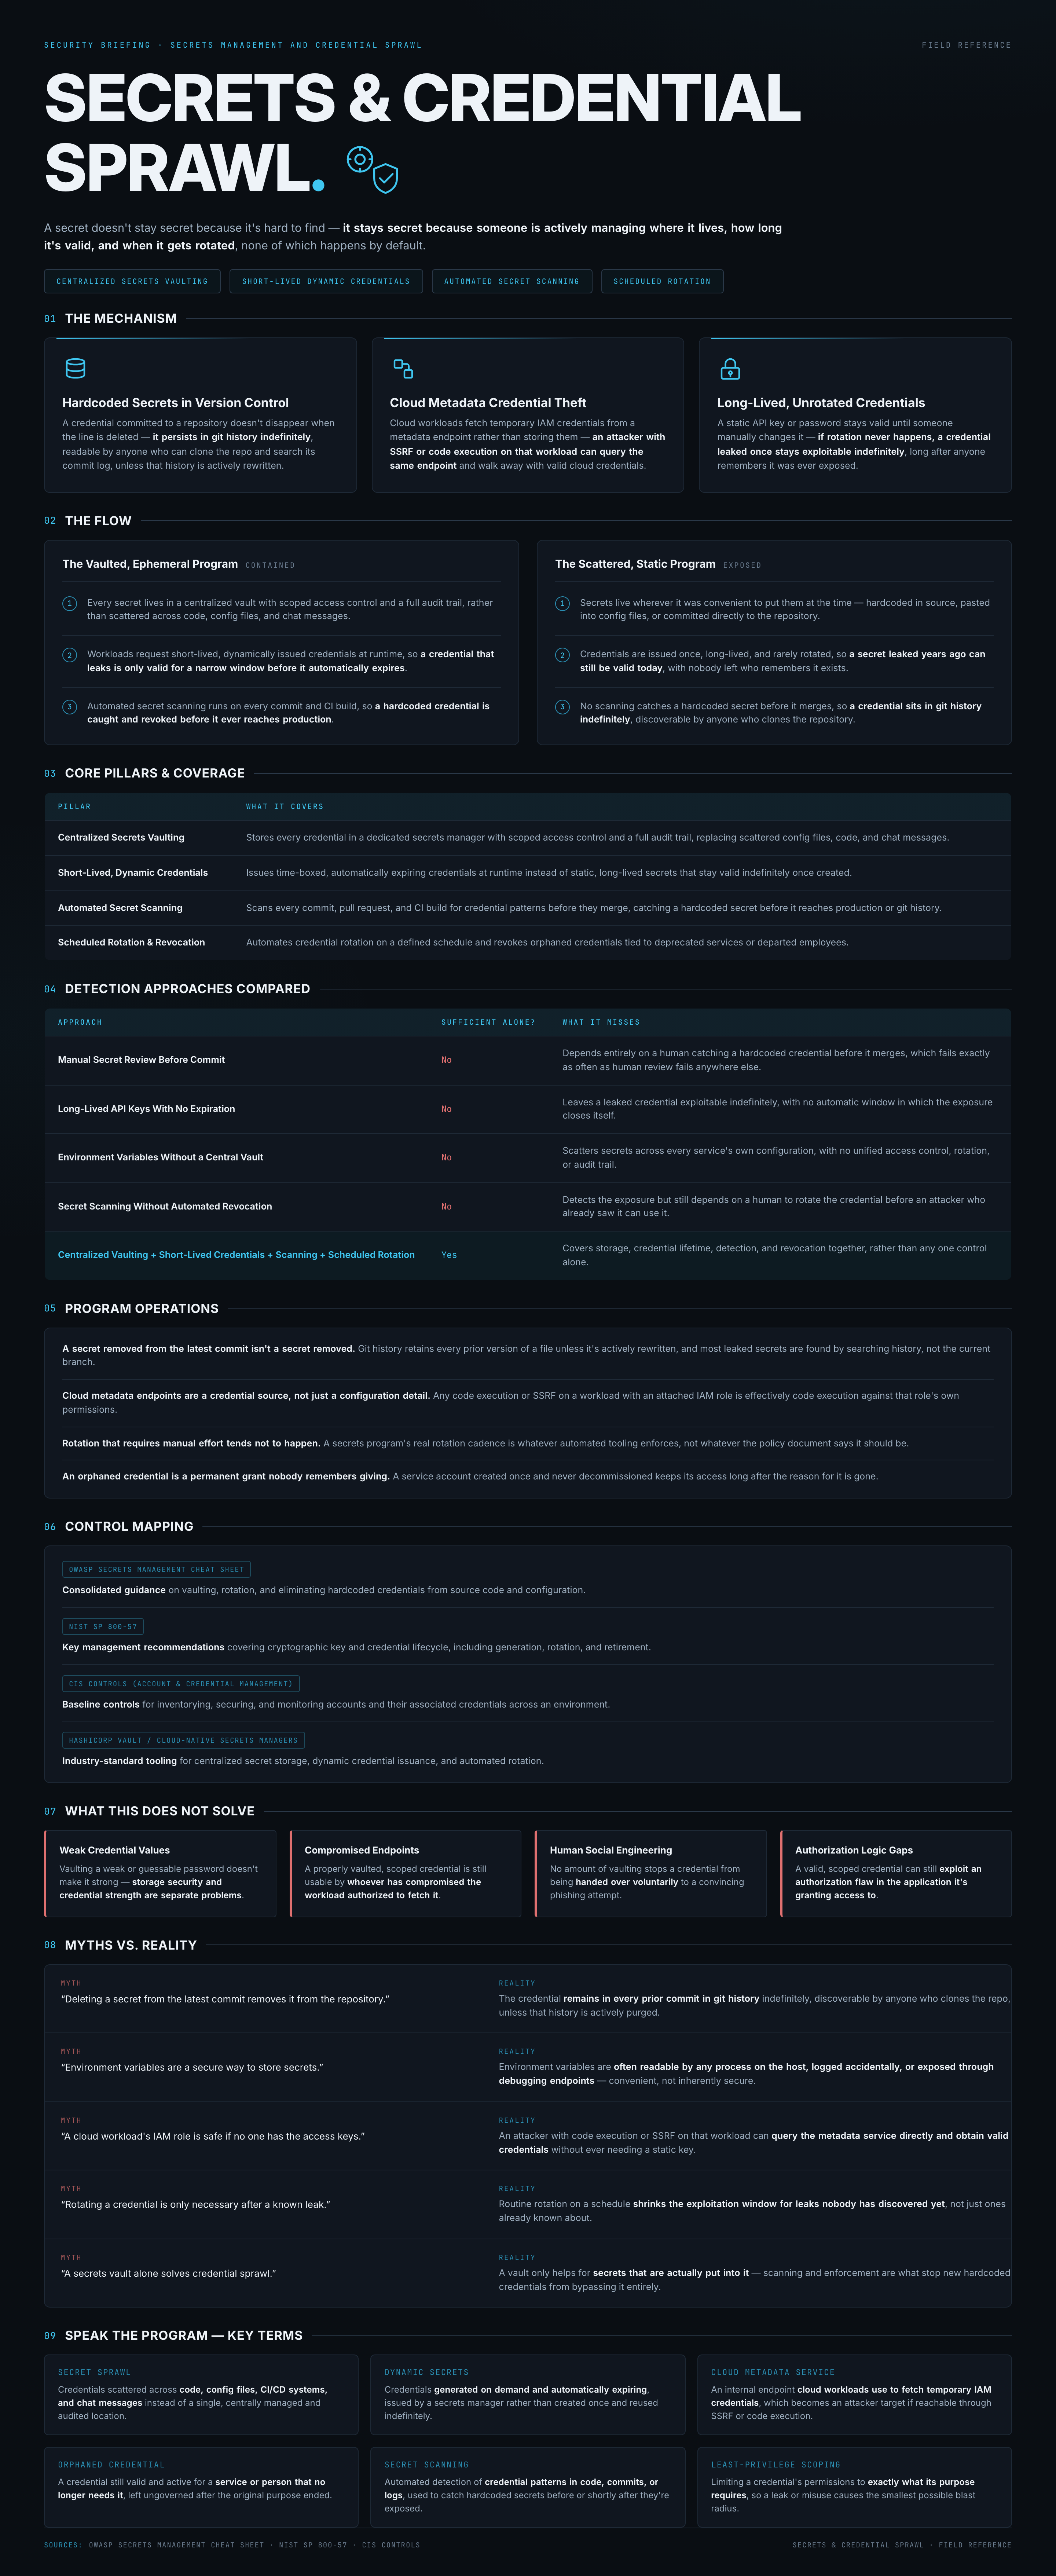
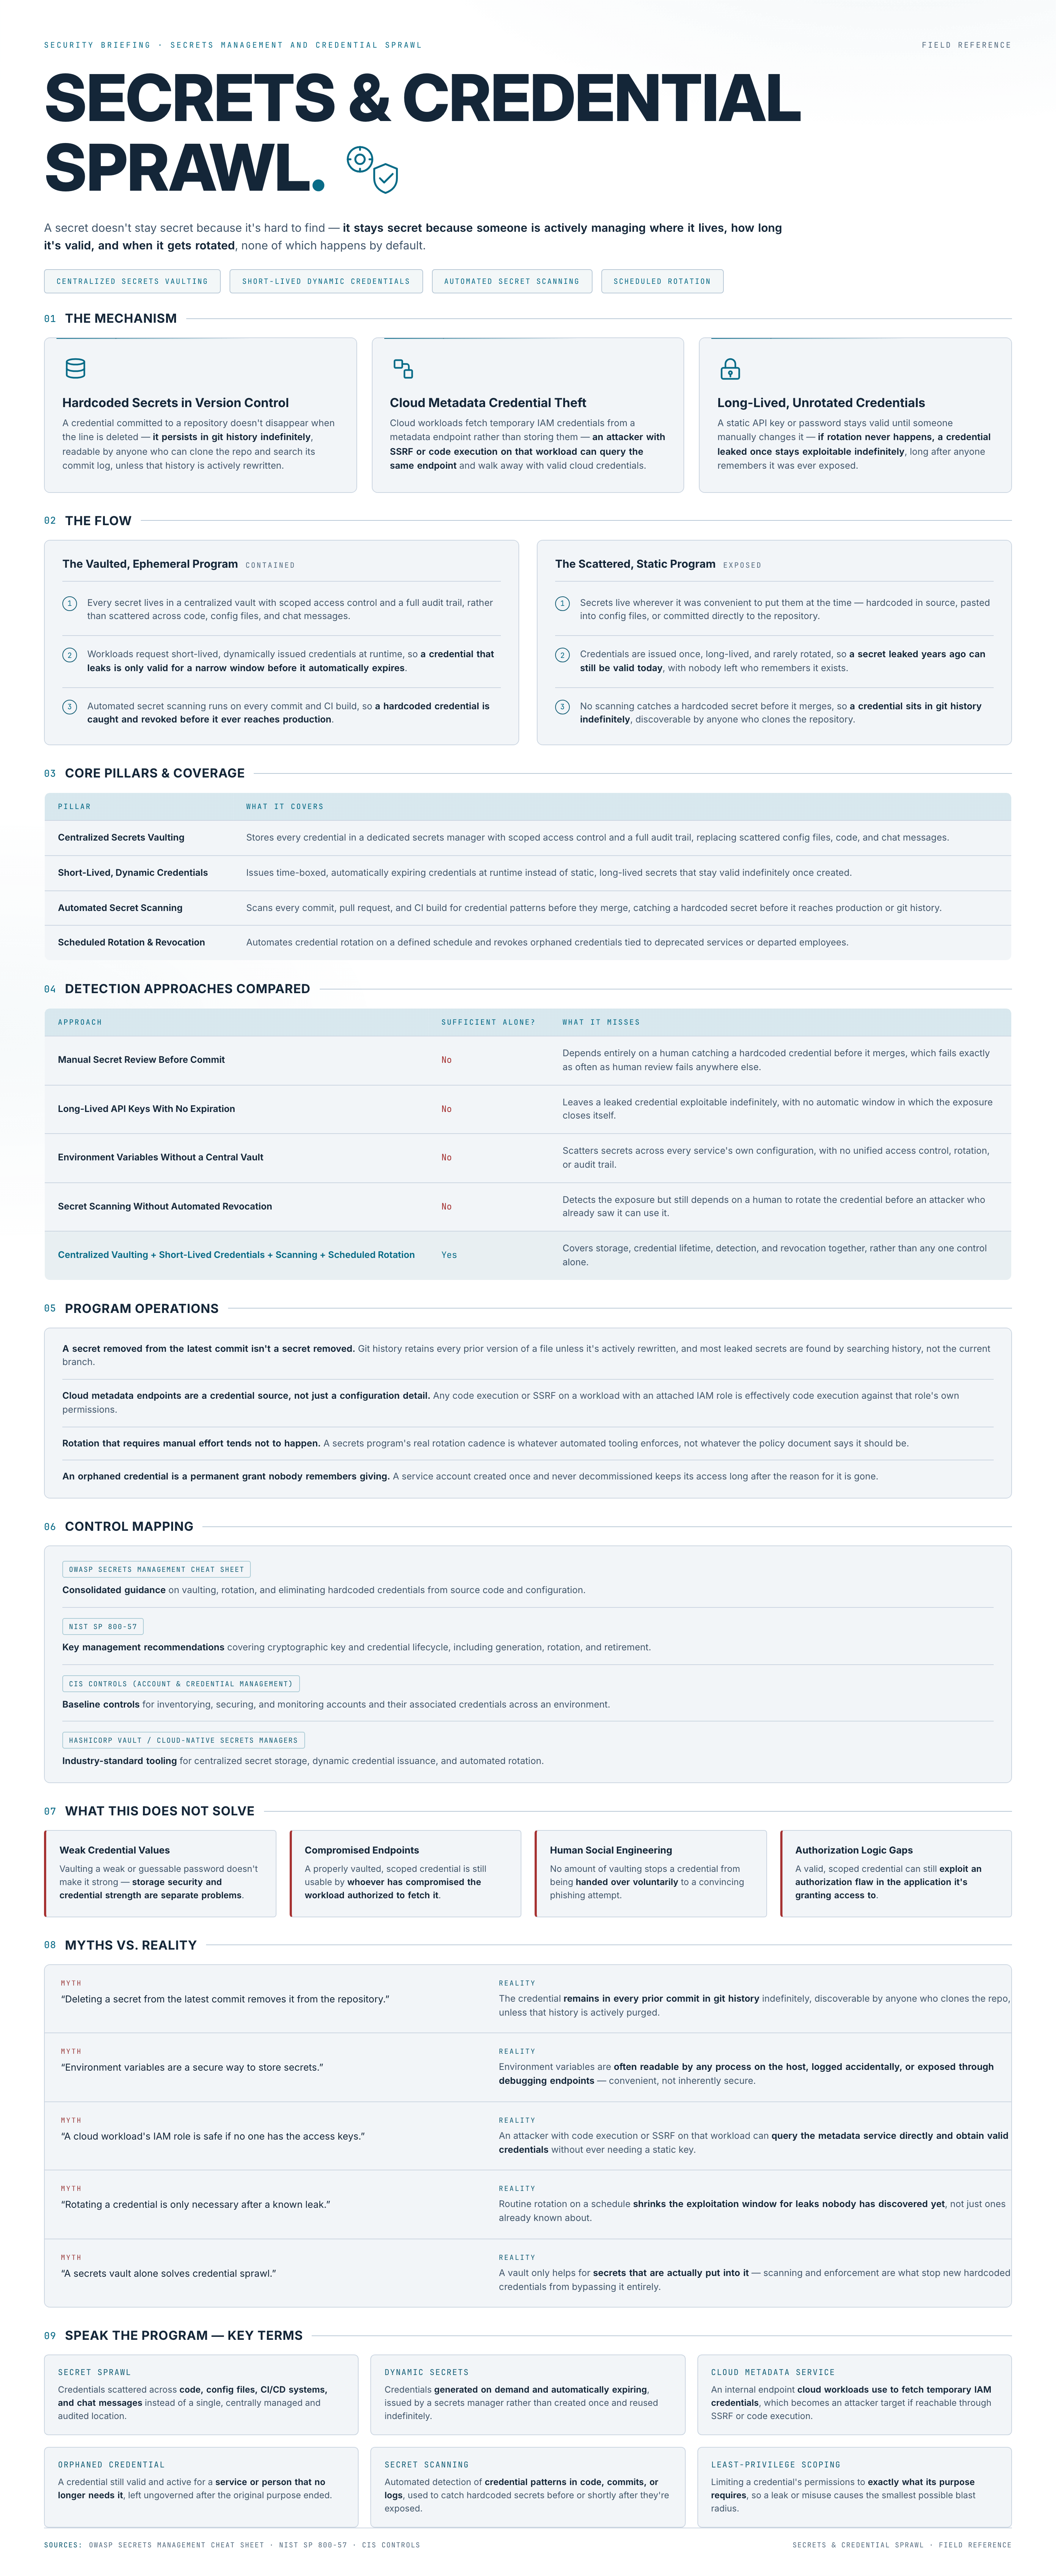
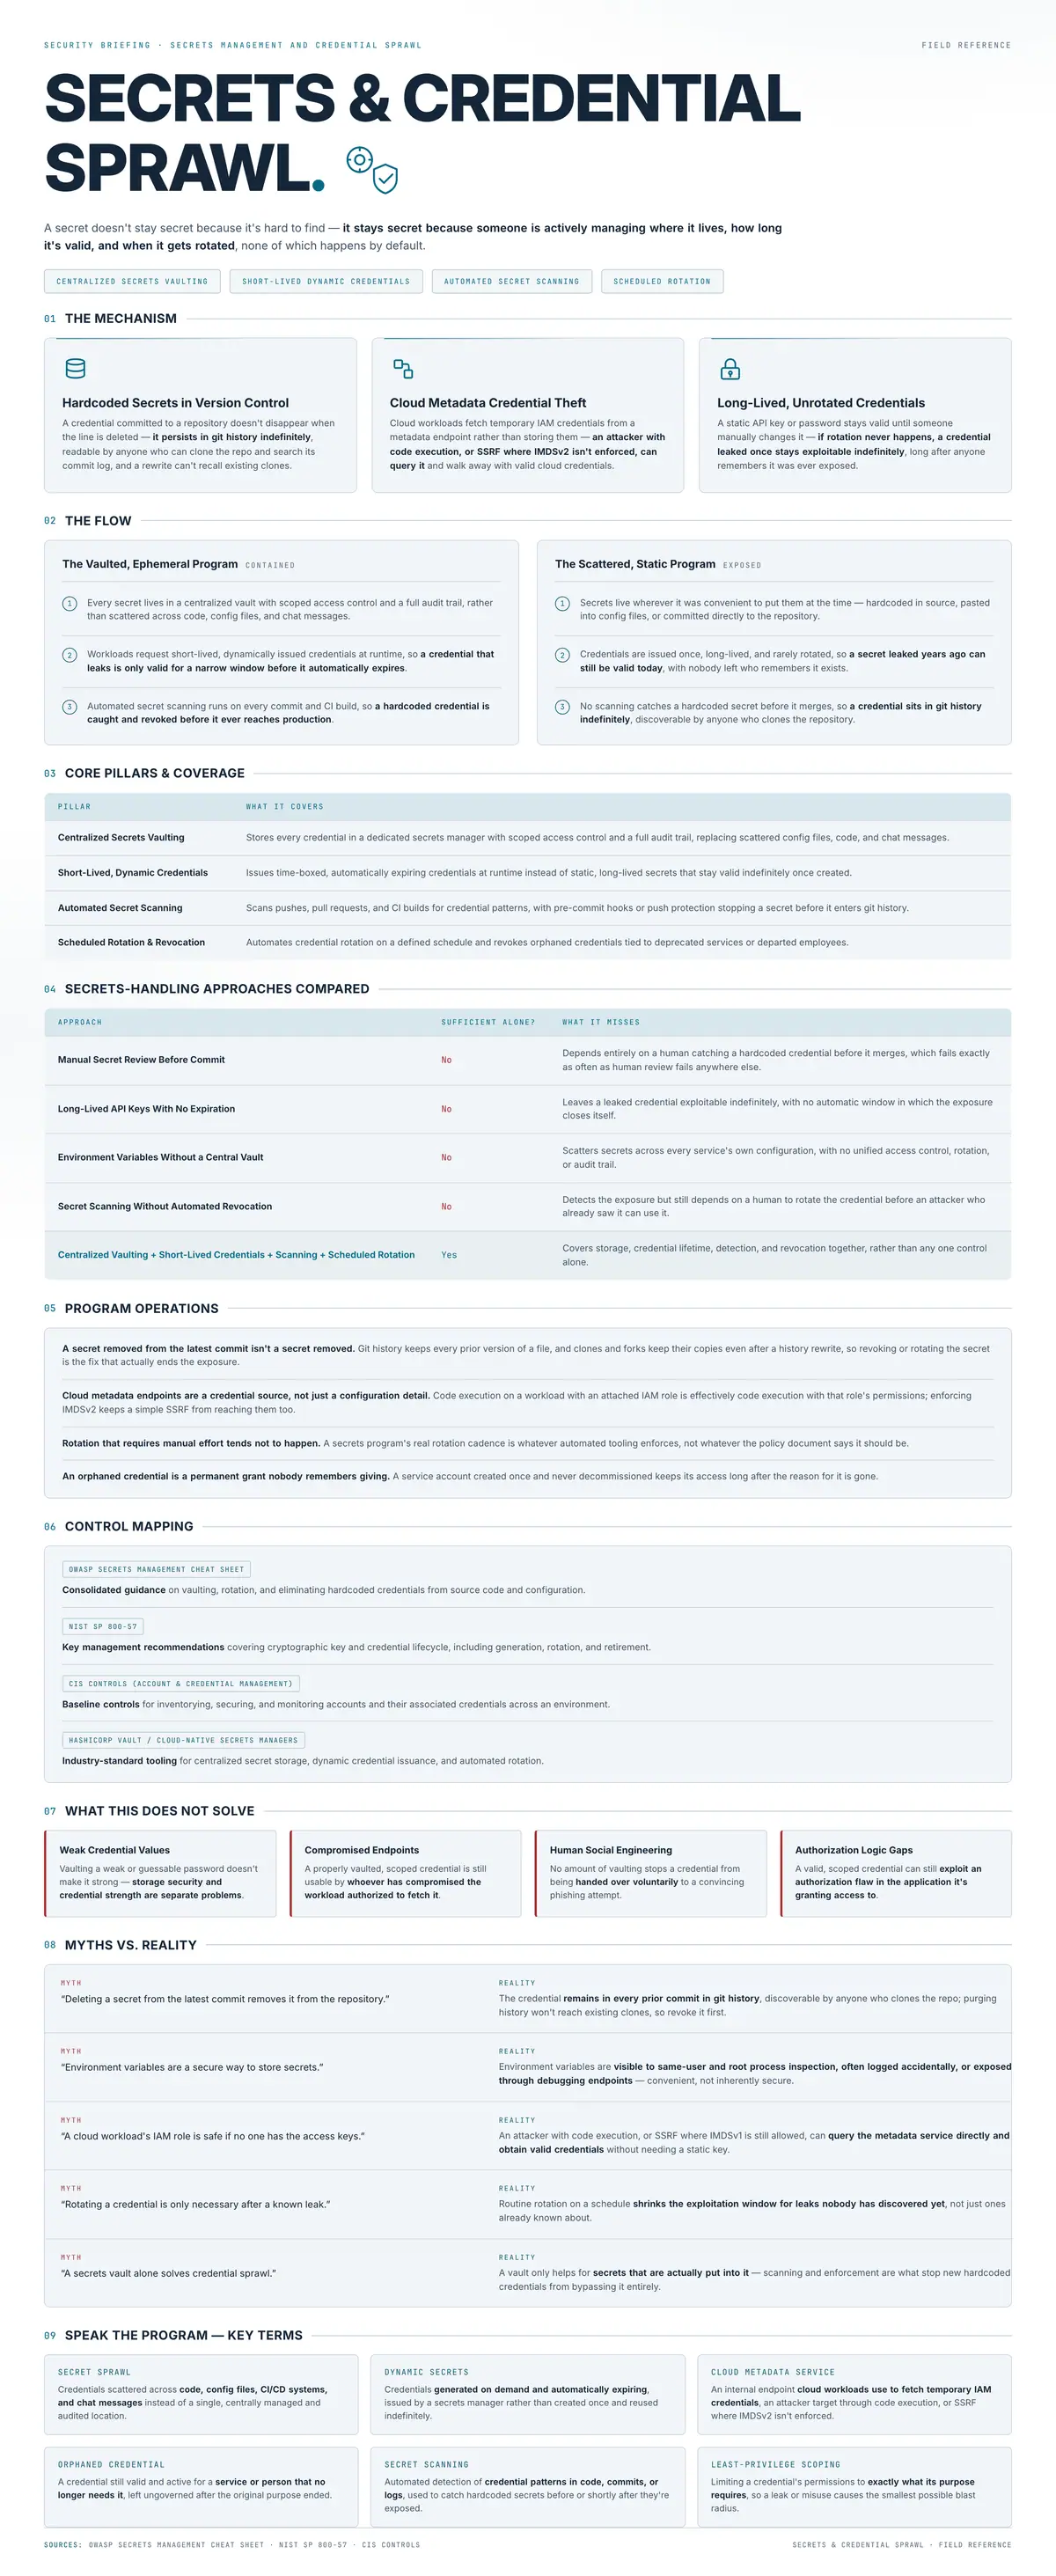
A secret doesn't stay secret because it's hard to find — it stays secret because someone is actively managing where it lives, how long it's valid, and when it gets rotated, none of which happens by default.
Phishing-resistant authentication built on public-key cryptography. The private key never reaches the server, syncs only end-to-end encrypted, and cannot be replayed by an attacker who captures the traffic.
Every account, role, and permission an organization grants is a potential path in — and the accounts nobody remembers to review are the ones attackers find first. IAM turns identity from a one-time provisioning task into a continuously governed control.
Every admin credential, service account, and root password is a high-value target — and standing privileged access is often the shortest path from one compromised login to full domain control. PAM replaces persistent admin rights with vaulted, time-bound, monitored elevation.
A password saved in the browser is only as safe as the device it lives on — a password manager decides whether that credential survives when the device doesn't.
An API key hardcoded once doesn't expire when the project ends — it stays valid in code, logs, and forgotten scripts until someone finds it, or someone else does.
Every API key, service account, and workload identity is a credential nobody logs into — non-human identity governance treats machine credentials with the same rigor as human ones, because attackers already do.