Application Security (AppSec)
Vulnerabilities are cheapest to fix before code ships — AppSec builds security checks directly into the development pipeline, catching flaws in code, dependencies, and configuration before they reach production.
Cybersecurity Infographic Series · Application and Software Security
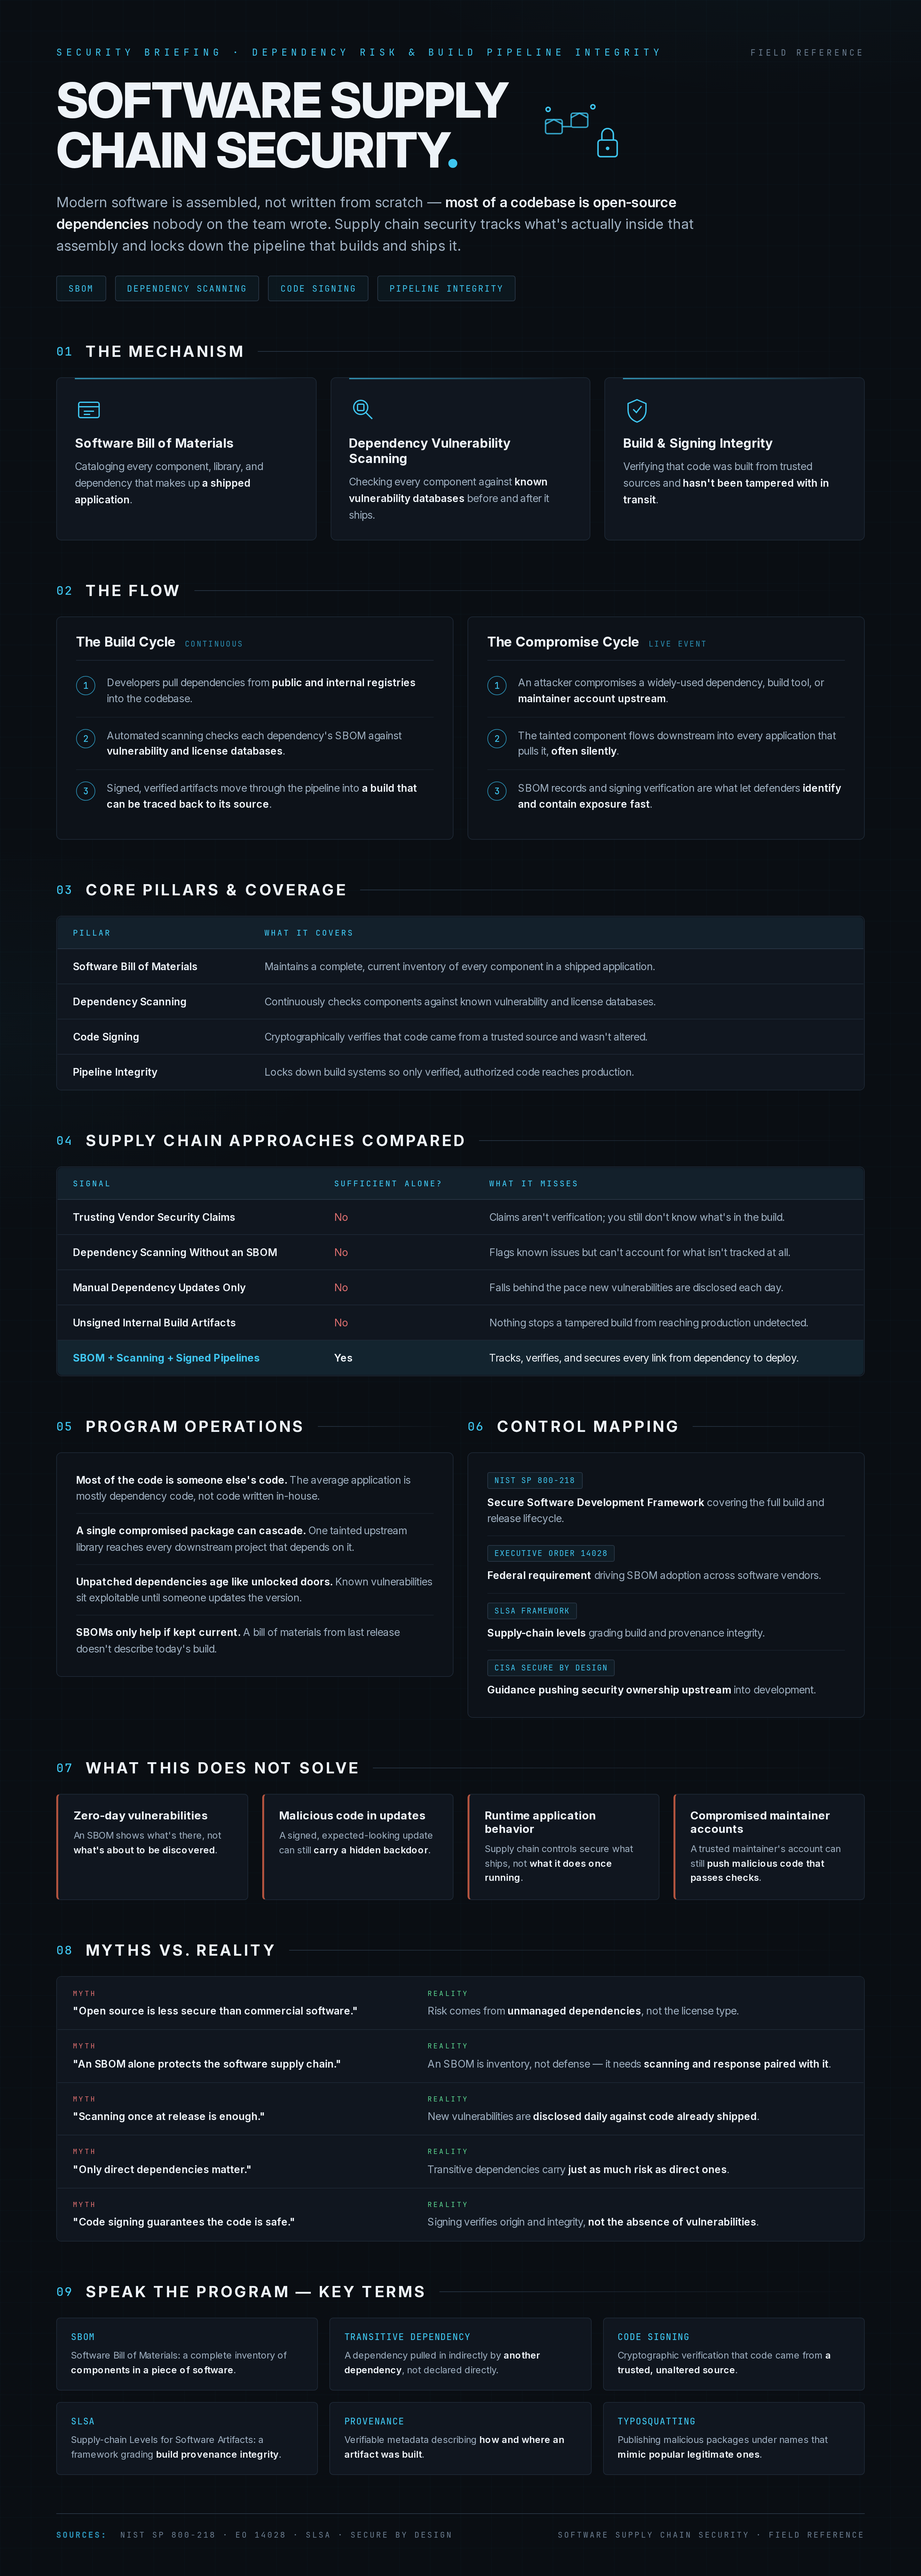
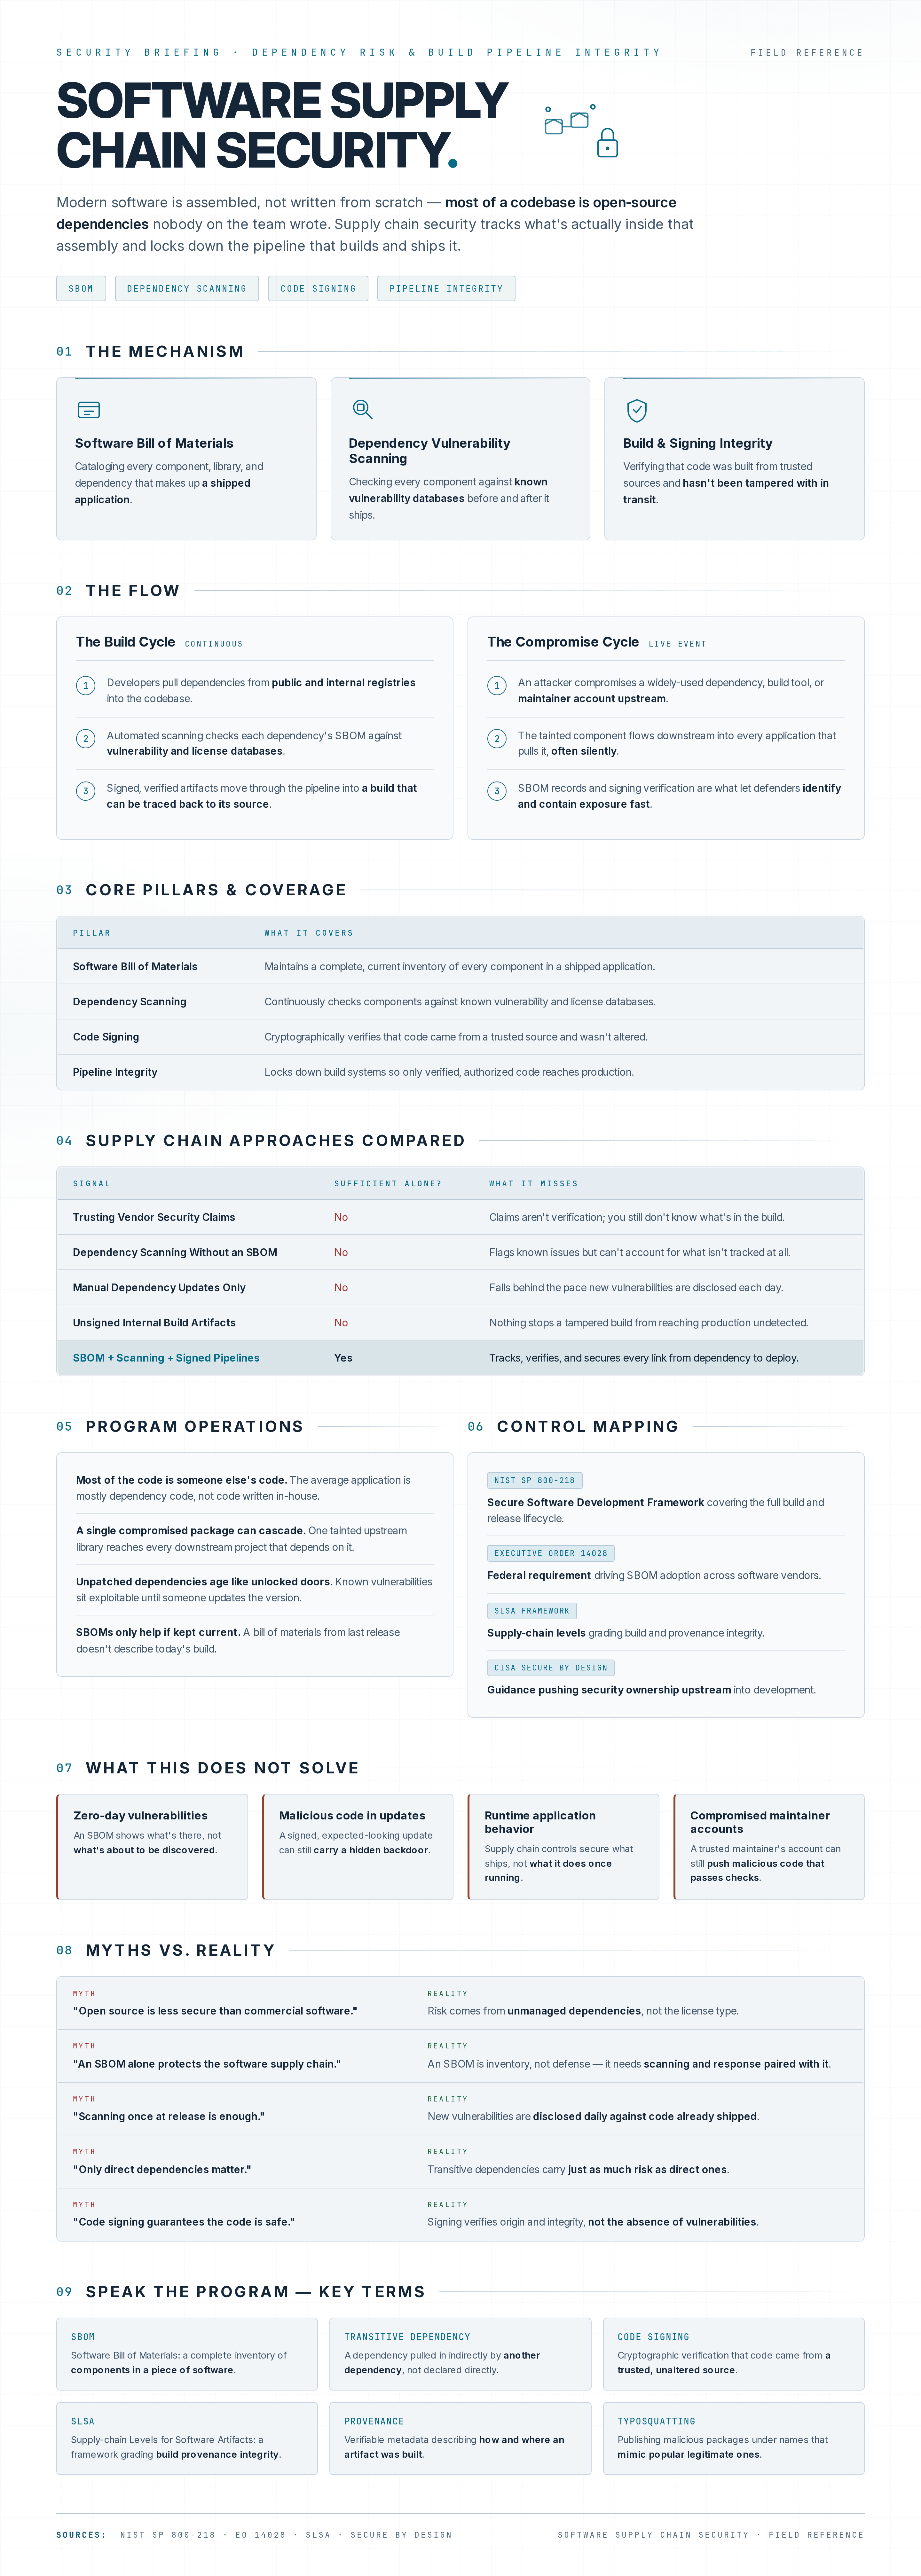
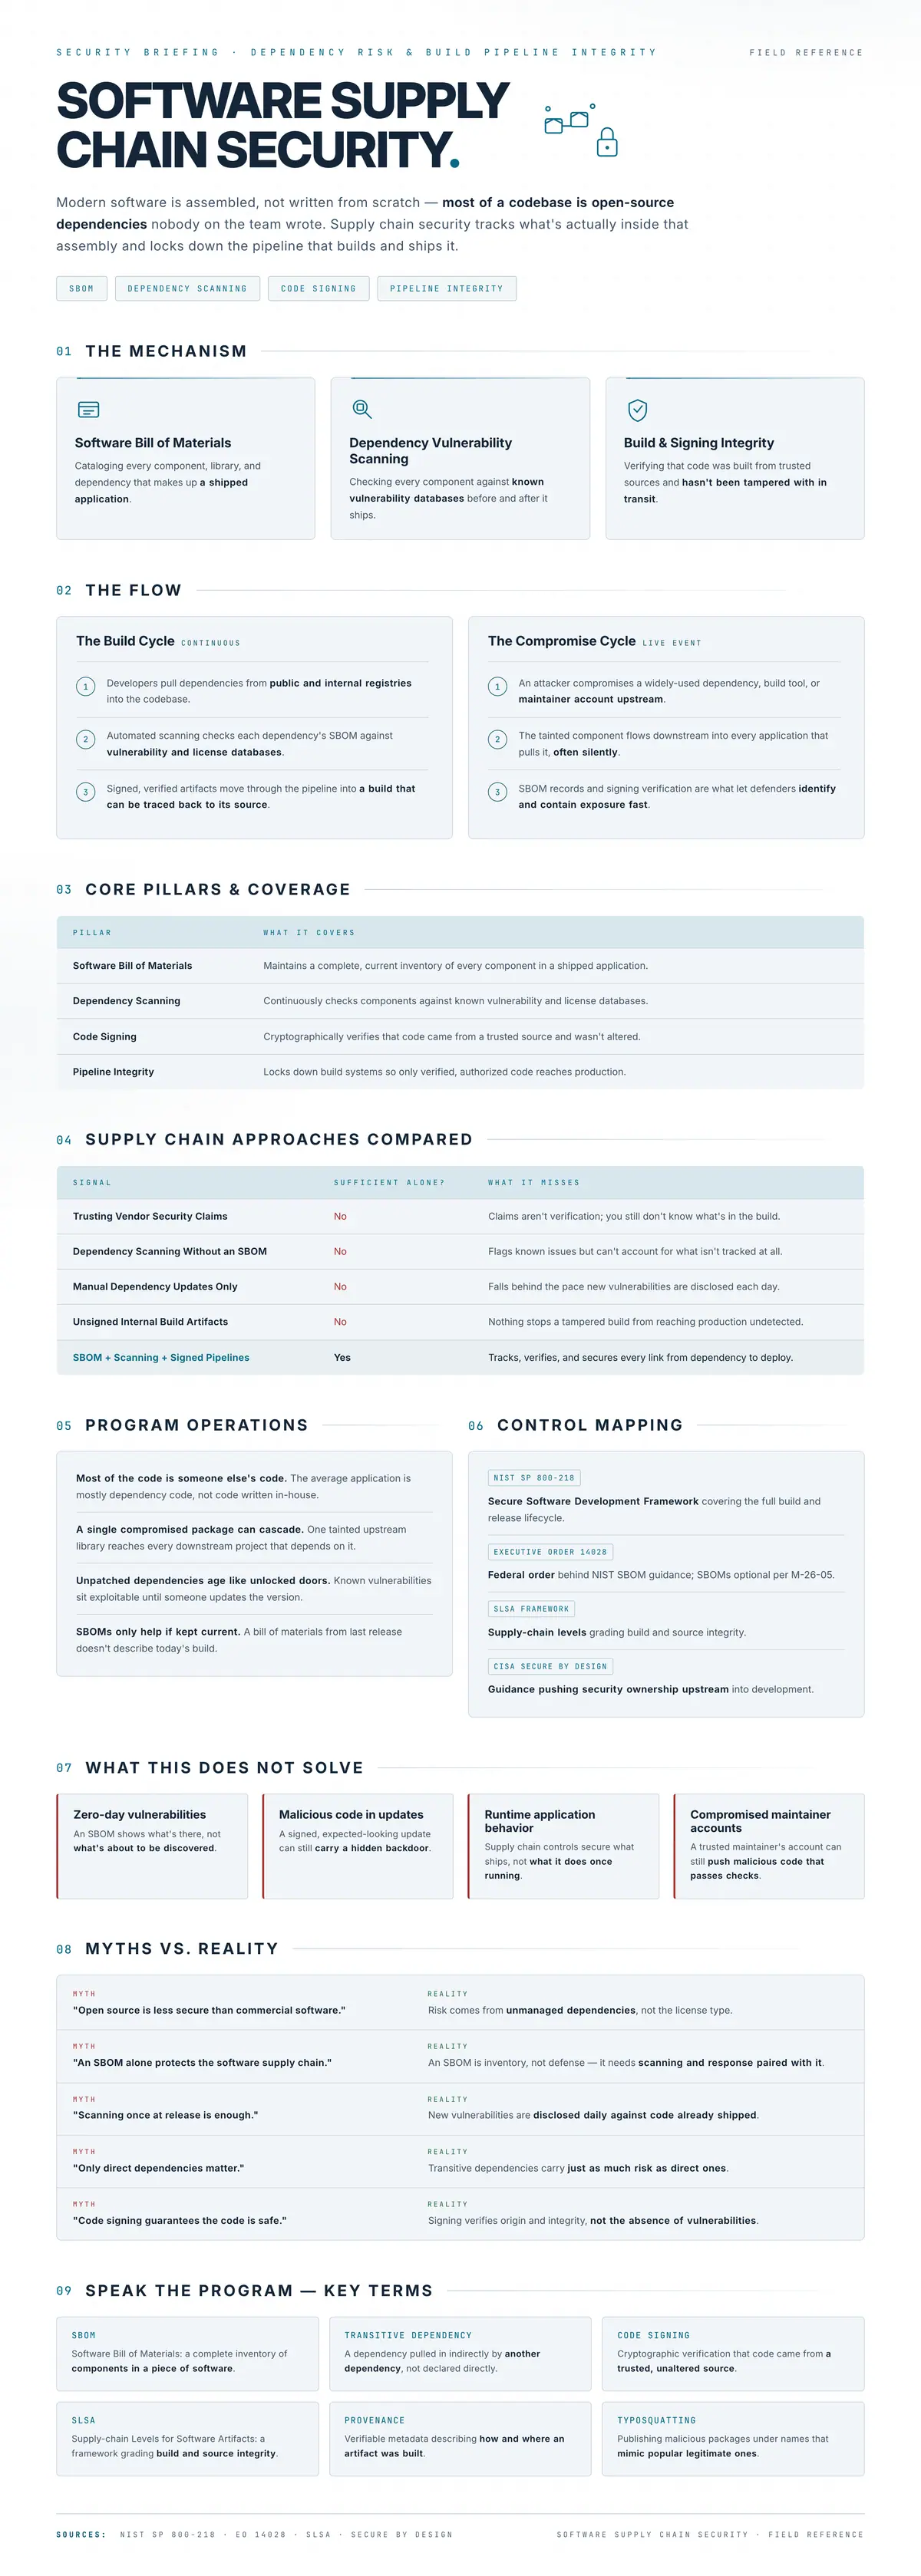
Modern software is assembled, not written from scratch — most of a codebase is open-source dependencies nobody on the team wrote. Supply chain security tracks what's actually inside that assembly and locks down the pipeline that builds and ships it.
Vulnerabilities are cheapest to fix before code ships — AppSec builds security checks directly into the development pipeline, catching flaws in code, dependencies, and configuration before they reach production.
Every API is a direct line into application logic and data — unauthenticated, unmonitored, or undocumented endpoints turn that convenience into an open door for attackers to walk through.
Shipping fast and shipping secure aren't in conflict — the fastest pipelines catch vulnerabilities before they reach a build artifact, not after a production incident.
A botnet defeats a per-IP rate limit just by spreading out — the real control isn't how many requests come from one address, it's whether the traffic behaves like the automation it actually is.
A single GraphQL request can nest, alias, and multiply its way to the computational cost of thousands — the danger isn't how many requests arrive, it's how much any one of them is actually allowed to ask for.
A webhook flips the usual direction of trust — the receiver has to authenticate a push it never asked for, and the sender has to make sure that push can't be pointed anywhere it shouldn't reach.